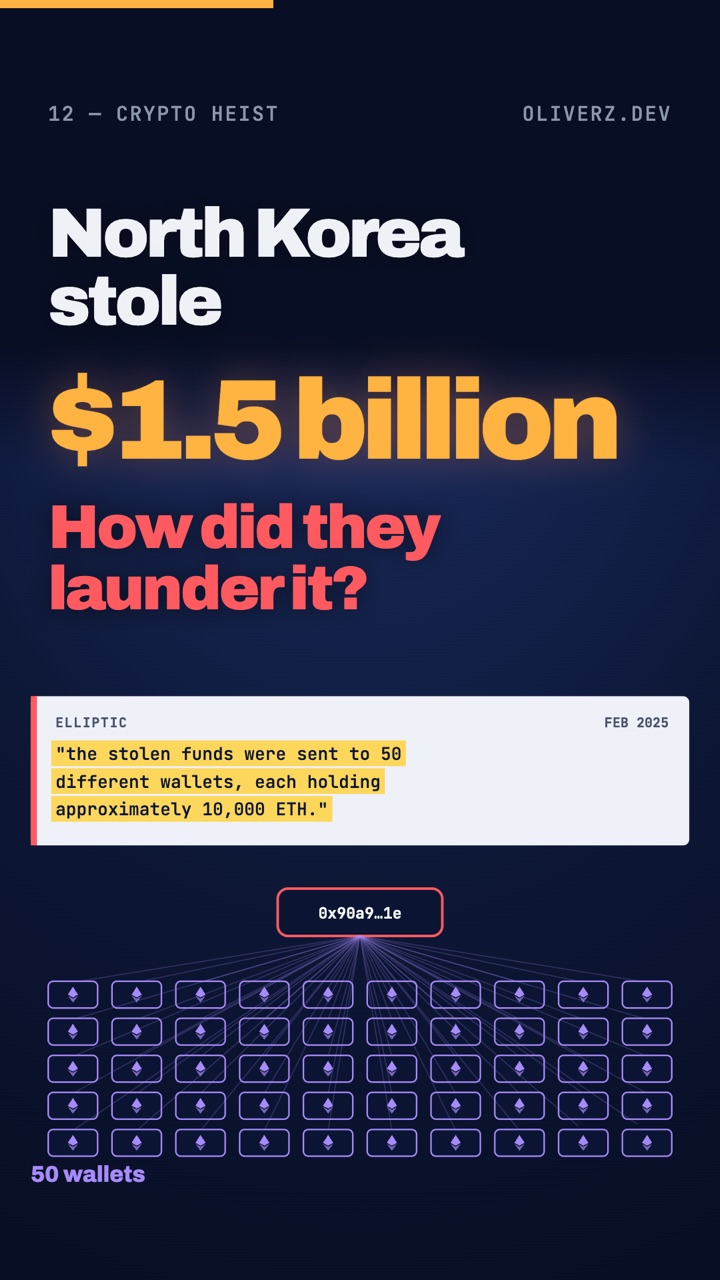
要点: 2025 年 2 月 21 日、FBI が北朝鮮によるものと断定したハッカーが、暗号資産取引所 Bybit から 1 件の取引で約 401,000 イーサ、およそ 15 億ドルを奪いました。資金洗浄は 3 つのステップで進みました。分割:2 時間以内にイーサは 50 のウォレットに分けられ、その後さらに多くのアドレスを経由して移されました。これは Lazarus が過去の資金洗浄で使ってきたピールチェーン(peel chain)のやり方です。形を変える:スワップサービス(その多くは THORChain を使うもの)を通じてイーサはビットコインに替えられ、9 日で 50 のウォレットはすべて空になりました。闇の中へ:ミキサーを経て、北朝鮮の過去のハッキングの盗品をすでに抱えていたアドレスへ。5 日目、FBI は北朝鮮の名を挙げ、取引所やブリッジにそれらのアドレスをブロックするよう求めました。
盗難:1 件の取引
FBI:"North Korea was responsible for the theft of approximately $1.5 billion USD in virtual assets from cryptocurrency exchange, Bybit, on or about February 21, 2025."(2025 年 2 月 21 日ごろ、暗号資産取引所 Bybit から約 15 億ドルの仮想資産が盗まれた件は、北朝鮮の犯行である。)Chainalysis はこれを "approximately 401,000 ETH"(約 401,000 ETH)としています。
侵入口は、Bybit が使っていたマルチシグサービス Safe{Wallet} でした。Sygnia の調査によると、"a macOS workstation belonging to a Safe{Wallet} developer… was compromised on February 4, 2025"(Safe{Wallet} の開発者の macOS ワークステーションが……2025 年 2 月 4 日に侵害された)。そして Safe のウェブ画面に仕込まれたコードには "an activation condition, set to execute the transaction manipulation only on a specific Bybit's cold wallet"(特定の Bybit のコールドウォレットに対してだけ取引の改ざんを実行するよう設定された発動条件)がありました。こうして "the Safe{Wallet} user interface displayed legitimate transaction data while malicious transactions were signed and executed."(Safe{Wallet} の画面には正規の取引データが表示される一方で、悪意ある取引が署名され実行された。)
ステップ 1:分割し、剥がしていく
Elliptic:"Within two hours of the theft, the stolen funds were sent to 50 different wallets, each holding approximately 10,000 ETH."(盗難から 2 時間以内に、盗まれた資金は 50 の異なるウォレットに送られ、それぞれが約 10,000 ETH を保有していた。)
そこから足跡はどんどん長くなります。ピールチェーンとは、米司法省の訴状を要約した 2020 年の記事の言葉を借りれば、"a single address begins with a relatively large amount of cryptocurrency. A smaller amount is then "peeled" off this larger amount… and the remainder is transferred to a one-time change address. This process is repeated – potentially hundreds or thousands of times"(ひとつのアドレスが比較的多額の暗号資産を持つところから始まる。そこから少額が「剥がされ」……残りは使い捨てのおつり用アドレスに移される。この過程が繰り返される。場合によっては数百回、数千回も)。Lazarus の古くからの手口です。Chainalysis はその 2020 年の事件についてこう書いています:"Lazarus collaborated with Tian and Li to launder the stolen cryptocurrency, conducting hundreds of transactions and forming peel chains that further obfuscated the path of funds."(Lazarus は Tian と Li と協力して盗んだ暗号資産を洗浄し、数百件の取引を行ってピールチェーンを形成し、資金の経路をさらにわかりにくくした。)
Bybit の資金についてピールチェーンを具体的に追跡した資料は確認できていないため、動画の中のチェーンはイメージです。FBI が実際に述べているのは、盗まれた資産が "dispersed across thousands of addresses on multiple blockchains."(複数のブロックチェーン上の数千のアドレスに分散された)ということです。
5 日目:FBI
2 月 26 日、FBI は北朝鮮の名を挙げ("FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor""、つまり FBI はこの北朝鮮の悪意あるサイバー活動を「TraderTraitor」と呼んでいる)、アドレスを公表しました:"The following Ethereum addresses are holding or have held assets from the theft, and are operated by or closely connected to North Korean TraderTraitor actors"(以下のイーサリアムのアドレスは、今回の盗難による資産を保有している、または保有していたもので、北朝鮮の TraderTraitor 実行者が運用しているか、それと密接に関係している)。私たちが数えたところ 51 個ありました。公告そのものは数を示していません。
FBI の要請は次のとおりです:"FBI encourages private sector entities including RPC node operators, exchanges, bridges, blockchain analytics firms, DeFi services, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder the stolen assets."(FBI は、RPC ノード運営者、取引所、ブリッジ、ブロックチェーン分析企業、DeFi サービス、その他の仮想資産サービス提供者を含む民間事業者に対し、TraderTraitor 実行者が盗まれた資産の洗浄に使っているアドレスとの取引、およびそこから派生する取引をブロックするよう促す。)
ステップ 2:形を変える
TRM Labs は 3 月 3 日にこう書いています:"All of the stolen ETH has now been moved to new addresses, with the vast majority bridged to Bitcoin, mostly via services using THORchain."(盗まれた ETH はすべて新しいアドレスに移され、その大半は主に THORchain を使うサービスを通じてビットコインへブリッジされた。)Elliptic は時間の経過を補っています。50 のウォレットは "were then emptied one by one over the next nine days. The last of the original 50 wallets holding the stolen funds was emptied on 3rd March."(その後 9 日間でひとつずつ空にされた。盗まれた資金を保有していた当初の 50 のウォレットのうち、最後のひとつが空になったのは 3 月 3 日だった。)
ステップ 3:闇の中へ
TRM:"We have now entered that second phase and have seen an initial tranche of Bybit's BTC being deposited to mixers including Wasabi and CryptoMixer."(現在は第 2 段階に入っており、Bybit 由来の BTC の最初の一部が Wasabi や CryptoMixer などのミキサーに預けられるのを確認している。)Elliptic:"this bitcoin has now begun to be passed through mixers, to further obfuscate the transaction trail."(このビットコインは、取引の足跡をさらにわかりにくくするため、ミキサーに通され始めている。)
そして、その資金は古い資金と合流しました。Chainalysis:"Funds from the Bybit exploit have also consolidated in addresses holding funds from other known DPRK-linked attacks, providing further evidence that the nation state actors are behind this latest incident."(Bybit への攻撃による資金は、北朝鮮が関与したとされる他の攻撃の資金を保有するアドレスにも集約されており、今回の事件の背後に国家レベルの実行者がいることを裏付けるさらなる証拠となっている。)
そして現金化、その使い道
最後のステップは、暗号資産を使えるお金に替えることです。国連専門家パネルが挙げるパターンのひとつは "Heavy reliance on third party launderers and over-the-counter brokers"(第三者の資金洗浄者や店頭(OTC)ブローカーへの強い依存)です。米財務省も "a PRC-based OTC virtual currency trader who facilitated the conversion of virtual currency stolen by DPRK actors working with the Lazarus Group to fiat currency."(Lazarus Group と組む北朝鮮の実行者が盗んだ仮想通貨を法定通貨に換えるのを手助けした、中国を拠点とする OTC 仮想通貨トレーダー)に制裁を科しました。
何のためのお金なのか。同じ国連報告書にはこうあります:"A second Member State reported that 40 per cent of the weapons of mass destruction programmes … are funded by illicit cybermeans."(別の加盟国は、大量破壊兵器計画の 40% が……不正なサイバー手段で資金を得ていると報告した。)これはある 1 か国がパネルに示した数字であり、パネル自身の結論ではありません。
たいていの始まり方
始まりはコードではなく、1 通のメッセージです。CISA:"The messages often mimic a recruitment effort and offer high-paying jobs to entice the recipients to download malware-laced cryptocurrency applications"(メッセージはしばしば採用活動を装い、高給の仕事をちらつかせて、受信者にマルウェア入りの暗号資産アプリをダウンロードさせようとする)。FBI が挙げる警告サインのひとつ:"Requests to conduct a 'pre-employment test' or debugging exercise that involves executing … scripts, or GitHub repositories."(……スクリプトや GitHub リポジトリの実行を伴う「採用前テスト」やデバッグ課題を求められること。)
- 見知らぬ人から送られてきたコードは、どんなに好条件の仕事の話でも実行しないこと。
- 署名する前に、取引の内容はそれを求めてきたウェブページではなく、デバイスそのものの画面で確認すること。
出典
- FBI IC3, North Korea Responsible for $1.5 Billion Bybit Hack, 26 Feb 2025
- Elliptic, The largest theft in history: following the money trail from the Bybit hack, Feb–Mar 2025
- TRM Labs, Bybit hack update: North Korea moves to next stage of laundering, 3 Mar 2025
- Chainalysis, Collaboration in the wake of record-breaking Bybit theft, 24 Feb 2025
- Chainalysis, New OFAC sanctions and DOJ complaint for North Korea-linked cryptocurrency laundering scheme, 5 Mar 2020
- Money Laundering Watch, Two Chinese nationals charged with laundering over $100 million in cryptocurrency for North Korea, 11 Mar 2020
- Sygnia, Sygnia's investigation into the Bybit hack
- UN Panel of Experts, S/2024/215, 7 Mar 2024
- US Treasury, jy1435, 24 Apr 2023
- CISA, AA22-108A: TraderTraitor; FBI, PSA 240903, 3 Sep 2024
動画はコードでアニメーションを作り、台本は AI の手を借りて書きました。上の引用はすべて出典で確認しています。51 個というアドレスの数は私たち自身が数えたものです。ウォレットのアドレス、各ホップの金額、ピールチェーン、画面、メッセージはイメージです。この記事は、FBI や分析企業が説明している水準で資金洗浄を解説するものであり、そのやり方を教えるものではありません。制作には Shotloop を使いました。コードで解説動画をつくり、1 ショットずつ直せる、私の無料 Mac アプリです。